Secure access for your CI/CD pipelines
Connect build runners to private networks, manage access rules as code, and share preview environments behind a login. No VPN profiles or open ports.


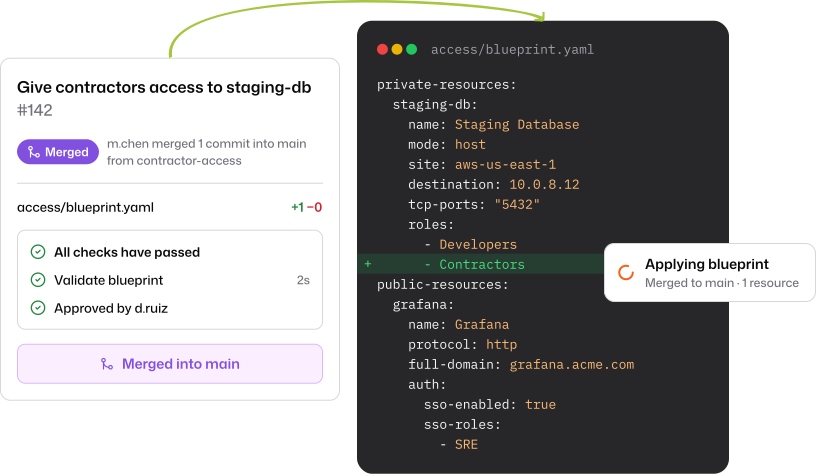
Manage access rules as code in Git
Define resources and who can reach them in a YAML file. Review changes in pull requests and let CI apply them.
Write access rules in YAML
Describe resources, targets, and roles in a blueprint file.
Apply changes from your pipeline
Run pangolin apply blueprint from GitHub Actions or any CI.
Start from what you have
Export your existing resources to a blueprint in one step.
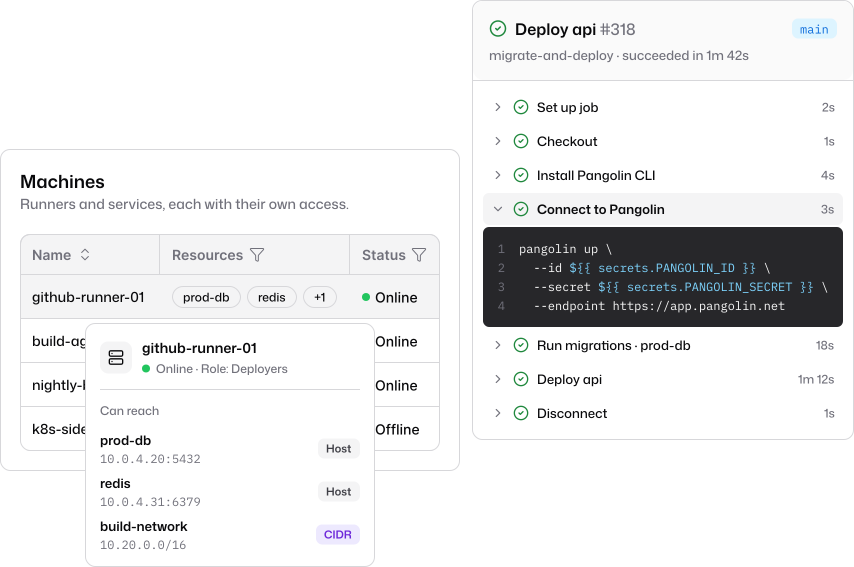
Connect runners and services to remote networks
Give CI runners, scripts, and background services their own login so they can reach private databases, servers, and APIs.
Access by role, like people
Each machine reaches only the resources its roles allow.
Credentials for each runner
No shared VPN profile. Revoke or rotate one runner without touching the rest.
Route a whole network
A Linux machine can share its connection with the build agents behind it.
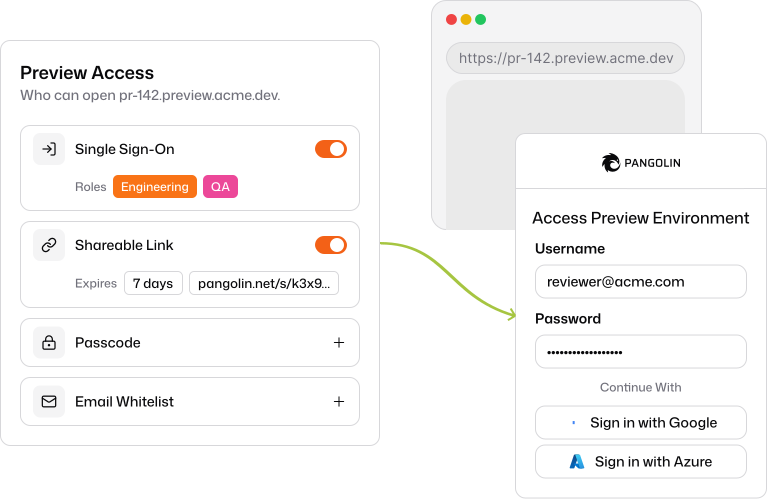
Share preview environments behind a login
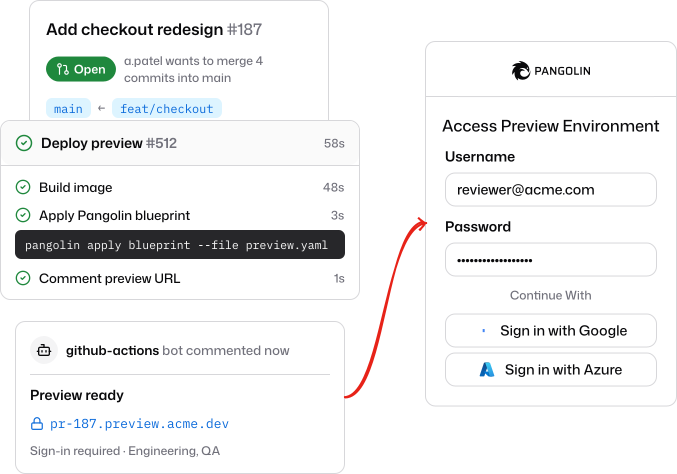
Give every preview environment its own private link. It’s created with the environment and removed when it goes away.
Created by your pipeline
The pipeline that spins up the environment also publishes its link.
Reviewers just sign in
Open the preview with single sign-on. No VPN or kubeconfig needed.
Never public
Previews stay off the open internet while they run.
Tools for automating access
Everything your pipelines need, with the same controls your people use.
Command-line tool
Apply blueprints and manage resources from scripts and CI.
Integration API
Create sites, resources, and access rules from your own code.
Runs in containers
Run connectors and clients as containers next to your workloads.
Docker Compose labels
Add labels to your services and Pangolin creates the resources for you.
Audit logs
See every change and connection, from people and pipelines alike.
Open source and self-hostable
Run Pangolin Cloud, or self-host the whole stack on your own infrastructure.
Explore other use cases
Remote Access
Identity-based access to private apps, servers, and networks.
Business VPN
Replace your legacy VPN with zero trust built on WireGuard®.
Reverse Proxy
Publish internal apps behind identity, without opening ports.
Securing AI
Identity-aware access to cloud and self-hosted models.
Zero Trust & Identity
Identity providers, roles, privileged access, and audit.
Privileged Access
Just-in-time SSH, browser RDP and VNC, and session logs.