Secure remote access for every team
Give employees, contractors, and machines identity-based access to private apps, servers, and networks, without exposing anything to the internet or opening a single port.


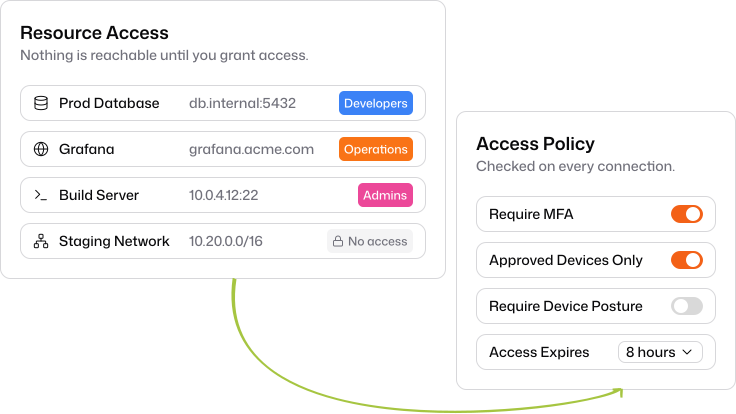
Granular access control
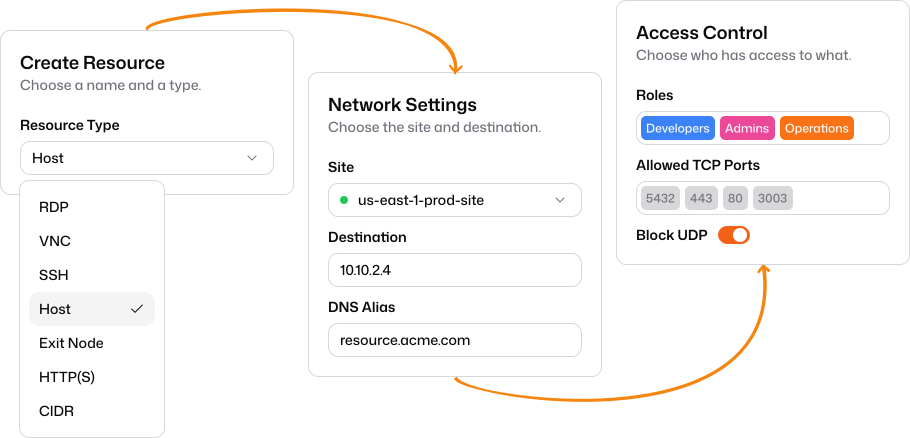
Decide who can reach what, from which device, and for how long. Access is granted per resource and nothing is reachable by default.
Identity-first security
Sign in with Google Workspace, Microsoft Entra ID, Okta, or any OIDC provider, with SSO and MFA.
Least privilege per resource
Assign roles on each resource. A user’s access is exactly the union of what their roles can reach.
Device posture and approvals
Check devices before they connect, and approve new devices before they get any access.
Connect anything, anywhere
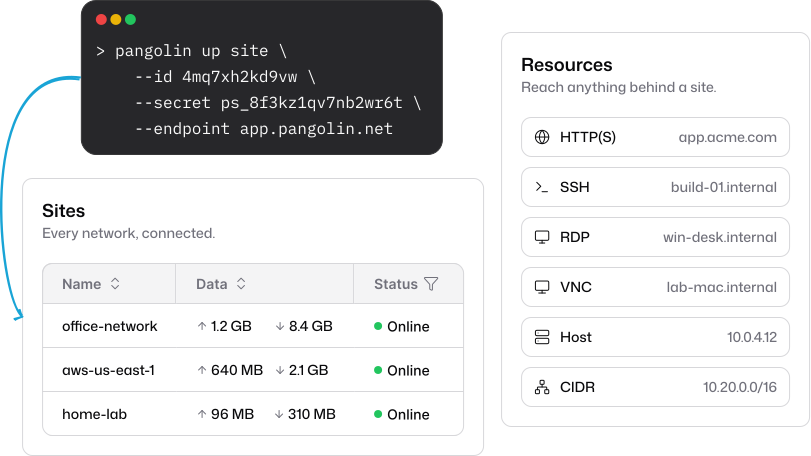
Reach private resources across clouds, datacenters, and offices from one client, or straight from the browser.
Clientless browser access
Open internal web apps, SSH terminals, and RDP or VNC desktops in the browser, with no client to install.
Built on WireGuard®
Clients connect peer-to-peer with NAT traversal, falling back to an encrypted relay only when needed.
Hosts, networks, and DNS aliases
Grant a single host and port range or a whole CIDR, and give private addresses friendly names.
Centralized management and automation
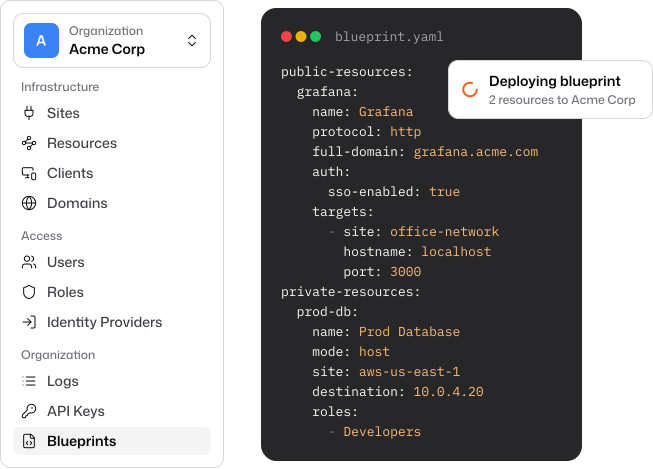
Run access for your whole organization from one dashboard, or manage it as code.
One dashboard
Manage users, roles, sites, resources, and policies in a clean, modern interface.
Blueprints and API
Define resources in declarative YAML or the integration API and roll them out from CI/CD.
Logs for every decision
Review access, network, and SSH session logs, or stream them to your SIEM on Enterprise.
Pangolin is better than a VPN
Organizations of every scale use Pangolin to unify and secure their distributed workforce, devices, and cloud workloads.
Identity-based access
Integrates with your existing identity provider to enable SSO and easy MFA.
Direct connectivity
Peer-to-peer connections between your users and your sites for better performance and reduced latency.
App & service exposure
Expose HTTP apps, TCP services, SSH, databases, and internal APIs with fine-grained controls.
Policy & visibility
Simple, human readable, and context-aware policies you can manage in one place.
A secure connection users don’t hate
Traditional VPNs and jump boxes cause friction for users. Pangolin stays out of the way by automating the identity-connection handshake.
Sign in with identity
Users authenticate through your IdP with SSO and MFA.
Connect to resources
Peer-to-peer tunnels reach apps and infrastructure without opening ports.
Enforce zero trust
Policies decide access in real time with full audit visibility.
Explore other use cases
Business VPN
Replace your legacy VPN with zero trust built on WireGuard®.
Reverse Proxy
Publish internal apps behind identity, without opening ports.
Securing AI
Identity-aware access to cloud and self-hosted models.
Zero Trust & Identity
Identity providers, roles, privileged access, and audit.
Privileged Access
Just-in-time SSH, browser RDP and VNC, and session logs.