Remote access for every device in the field
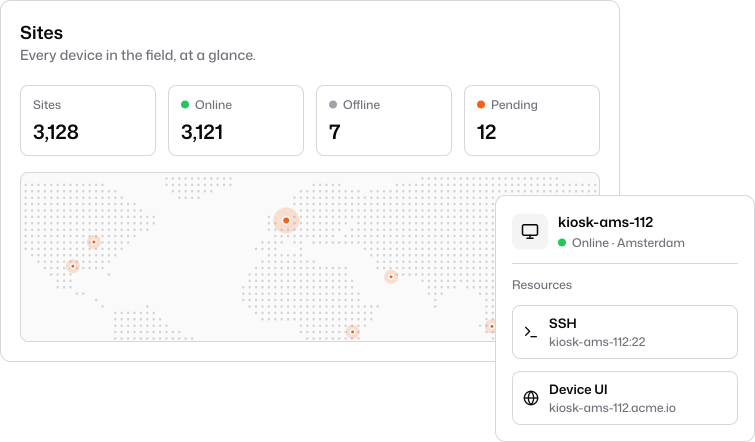
Provision thousands of edge devices from one golden image and reach them over SSH, HTTP, or remote desktop, without port forwarding, static IPs, or VPN boxes.


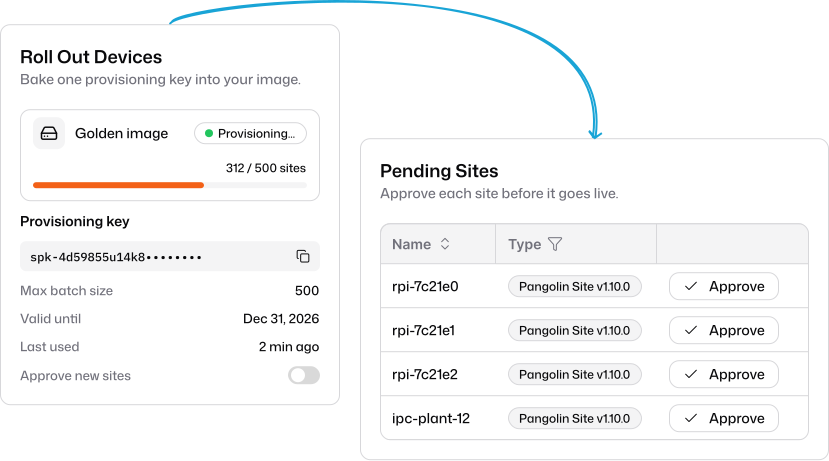
Provision fleets from a golden image
Ship one generic image. On first boot, each device trades a shared provisioning key for its own credentials and registers itself.
Provisioning keys
Set a validity period, a usage limit, and whether new sites are approved automatically.
Unique credentials per device
The key is exchanged and wiped on first boot, so one compromised device never exposes the fleet.
Approve before production
Hold new sites in a pending state until an admin reviews and approves them.
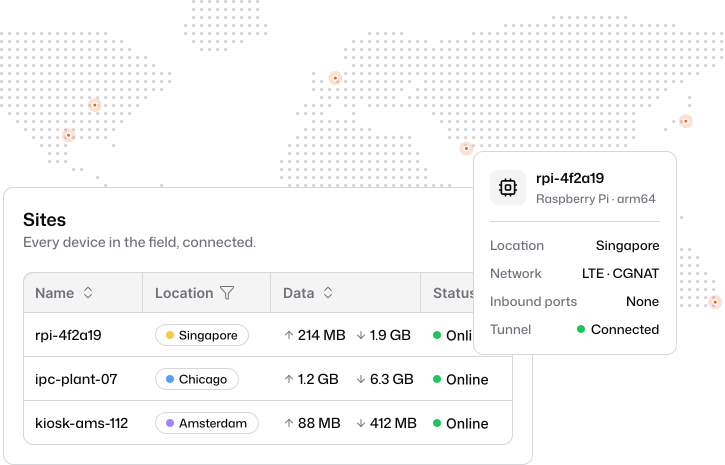
Reach devices behind any network
Devices connect outbound, so they work behind NAT, carrier-grade NAT, and firewalls you don’t control.
No open ports
Nothing on the device or the network around it accepts inbound connections.
SSH, HTTP, RDP, and more
Expose a device’s terminal, web interface, or remote desktop as a resource.
A lightweight connector
Runs as a single binary or container on ARM and x86, from a Raspberry Pi to an industrial PC.
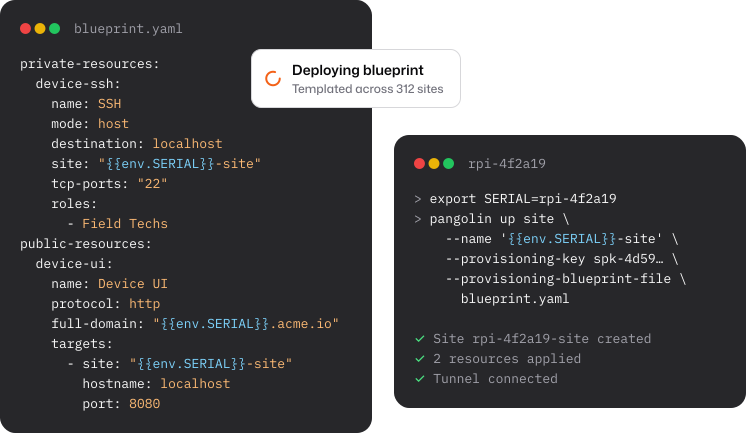
Configure every device as code
Blueprints with environment variables give each device its own resources, domains, and access rules automatically.
Templated blueprints
Variables like the device serial number name each site, alias, and domain.
Roles, not one-off grants
Grant access to roles once, and every new device picks it up.
Integration API
Automate rollouts and audits from your own tooling.
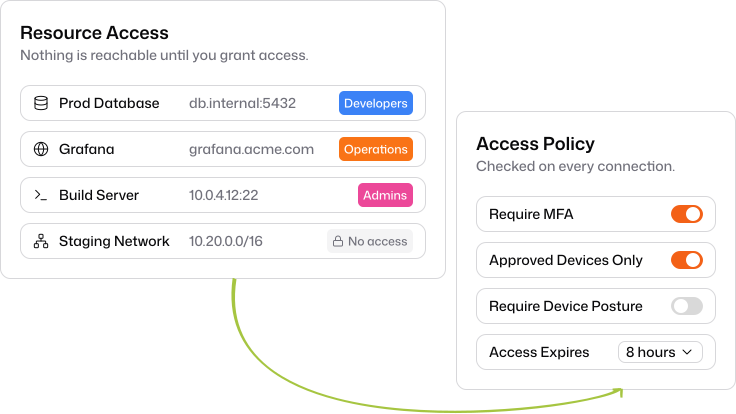
Scoped access for technicians and contractors
Give support staff and outside contractors access to the devices they service, and nothing else.
Separate sites stay separate
Keep each location, customer, or building isolated from the others.
Tied to a person
Every connection is authenticated with your identity provider and logged.
Revoke in seconds
End access the moment a job is done, with no hardware or shared credentials to collect.
Built for fleets in the field
From a few gateways to thousands of devices across sites you don’t control.
Outbound-only connections
Works behind NAT, CGNAT, and customer firewalls without port forwarding.
Per-device identity
Every device gets its own credentials you can rotate or revoke on its own.
Labels and search
Tag sites by customer, region, or device class and filter the whole fleet.
Browser-based access
Open a device’s SSH terminal or web UI in the browser, with no client to install.
Audit logs
See who connected to which device and when, or stream it to your SIEM.
Open source and self-hostable
Run Pangolin Cloud, or self-host the whole stack on your own infrastructure.
- 3,100+
- Remote Linux hosts managed by Lumistry
- 100+
- Retail locations connected for Gill Capital and H&M
- 100
- Properties rolled out by Fidelity in year one
Explore other use cases
Remote Access
Identity-based access to private apps, servers, and networks.
Business VPN
Replace your legacy VPN with zero trust built on WireGuard®.
Reverse Proxy
Publish internal apps behind identity, without opening ports.
Securing AI
Identity-aware access to cloud and self-hosted models.
Zero Trust & Identity
Identity providers, roles, privileged access, and audit.
Privileged Access
Just-in-time SSH, browser RDP and VNC, and session logs.