WireGuard® for business, without the busywork
Pangolin turns WireGuard® into a secure, identity-aware network for your whole organization. Keep the speed and simplicity of WireGuard® and skip the key distribution, config files, and port forwarding.


Pangolin elevates the WireGuard® experience
WireGuard® is a fast, modern, and audited tunnel. Running it for a whole company means managing keys, peers, routes, and access by hand. Pangolin handles all of that for you.
WireGuard® as a service
A managed control plane generates and distributes keys for every user, device, and site. No config files to copy around.
Identity-aware network
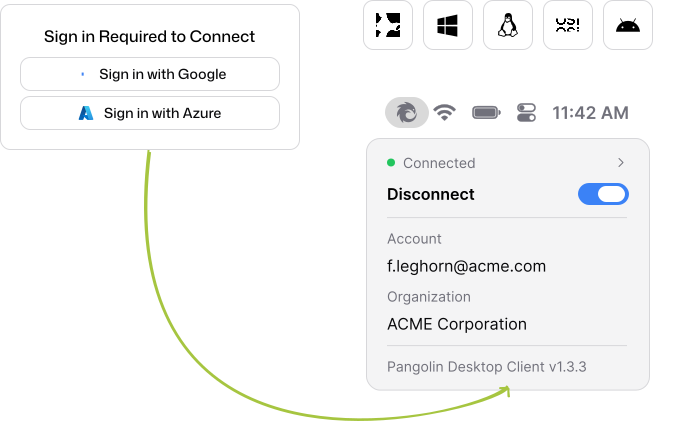
Users sign in with your identity provider, and their access follows them as they join, change teams, or leave.
Infrastructure agnostic
Connect on-premises, hybrid, and multi-cloud networks, with clients for macOS, Windows, Linux, iOS, and Android.
Fast, direct WireGuard® connections
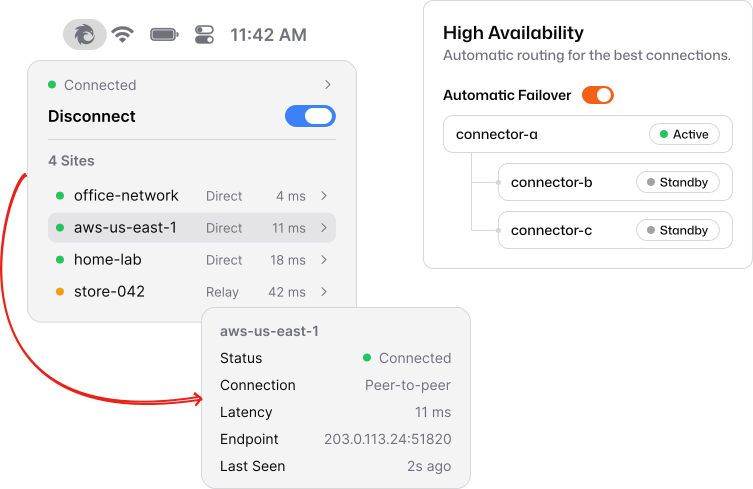
Clients and sites find each other and connect peer-to-peer, so traffic takes the shortest path instead of hairpinning through a concentrator.
NAT traversal built in
Connect through firewalls and NAT without opening inbound ports or assigning public IPs.
Encrypted relay fallback
When a direct path isn’t possible, traffic relays through a node and stays encrypted end to end.
High availability
Route resources through multiple sites and fail over automatically when one goes offline.
Enforce the principle of least privilege
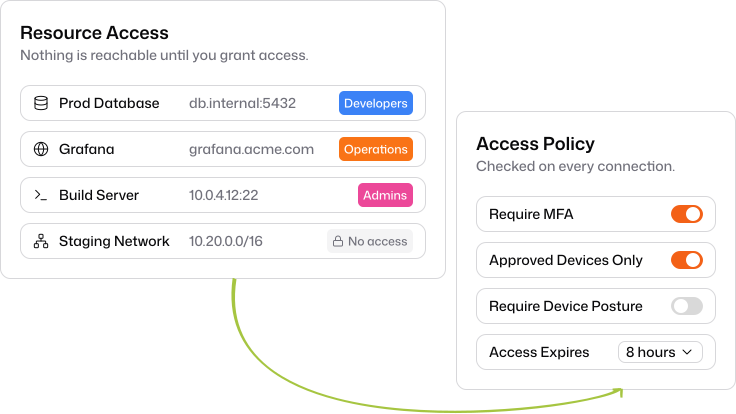
Plain WireGuard® gives a peer everything its allowed IPs cover. Pangolin grants access per resource, by role, and denies everything else.
Deny by default
Nothing is reachable until you define a resource and grant access to it.
Roles from your IdP
Map identity provider groups to roles and assign roles to hosts, ports, and ranges.
Device posture and approvals
Check devices before they connect, and approve new devices before they get any access.
Manage access policies as code
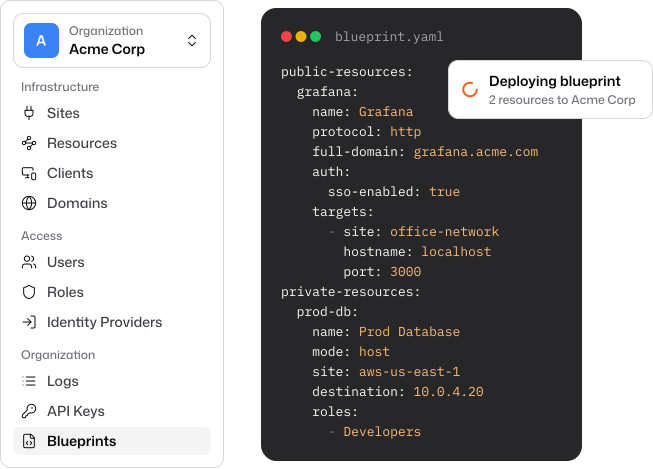
Fit network access into the DevOps workflows you already run, with version control and automated rollouts.
Declarative blueprints
Define sites, resources, and access in YAML and review changes like any other code.
Integration API
Automate users, roles, and resources from CI/CD or your own tooling.
One dashboard
Or manage everything from a clean, modern interface when that’s faster.
Gain visibility into network activity
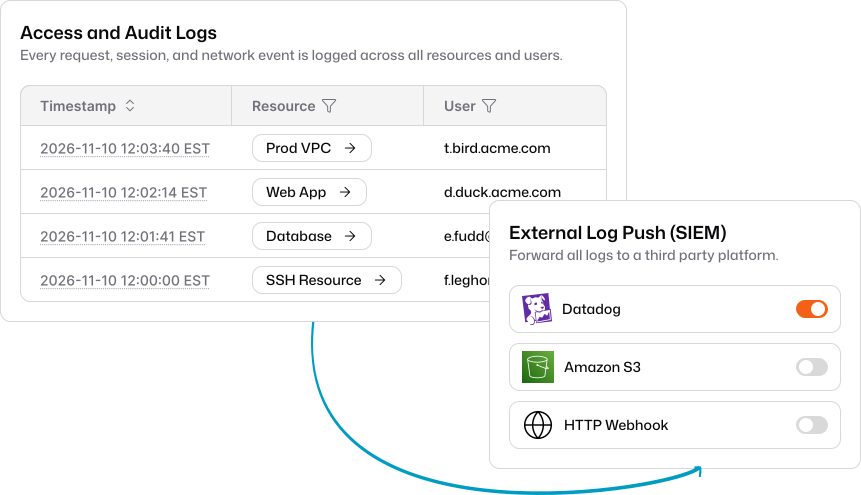
Know who connected to what, when, and from where, and who changed the policies that allowed it.
Network and access logs
See every connection and access decision across your WireGuard® network.
Admin action logs
Track every change to users, roles, resources, and settings.
Stream to your SIEM
Export logs or stream them to your SIEM, with configurable retention.
The WireGuard®-based network to protect your organization
Everything you need to run WireGuard® for a team of five or five thousand.
Peer-to-peer connections
Low-latency WireGuard® tunnels directly between clients and sites.
End-to-end encryption
Traffic is encrypted with WireGuard® from device to destination, even over relays.
Friendly DNS names
Give private hosts aliases like db.internal instead of remembering IP addresses.
Access policies for every resource
Role-based access to hosts, ports, and CIDR ranges across every network.
SSO with your identity provider
Google Workspace, Microsoft Entra ID, Okta, or any OIDC provider, with MFA.
Open source and self-hostable
Run Pangolin Cloud, or self-host the whole stack on your own infrastructure.
Explore other use cases
Remote Access
Identity-based access to private apps, servers, and networks.
Business VPN
Replace your legacy VPN with zero trust built on WireGuard®.
Reverse Proxy
Publish internal apps behind identity, without opening ports.
Securing AI
Identity-aware access to cloud and self-hosted models.
Zero Trust & Identity
Identity providers, roles, privileged access, and audit.
Privileged Access
Just-in-time SSH, browser RDP and VNC, and session logs.