Secure networking for managed service providers
Give each client an isolated, identity-based network in minutes. Replace legacy VPNs and per-client infrastructure with one platform you run for your whole book of business.


A VPN Built For MSPs
Pangolin was built from the ground up in the open with constant feedback from managed providers. The result? The best networking ecosystem for you and your clients.
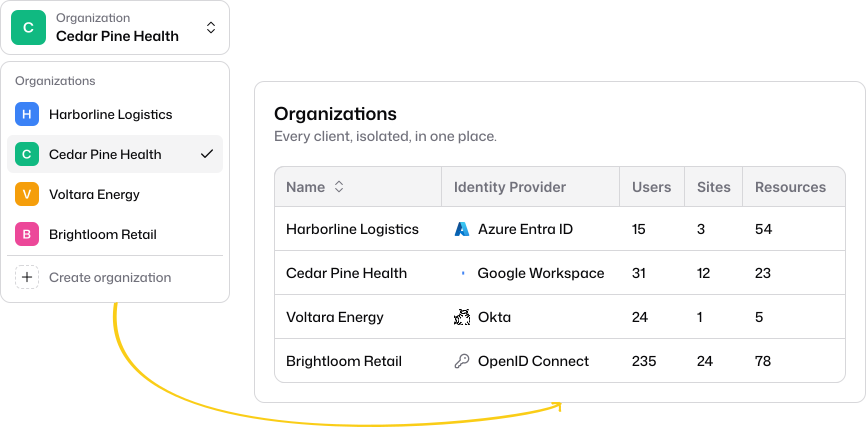
One organization per client
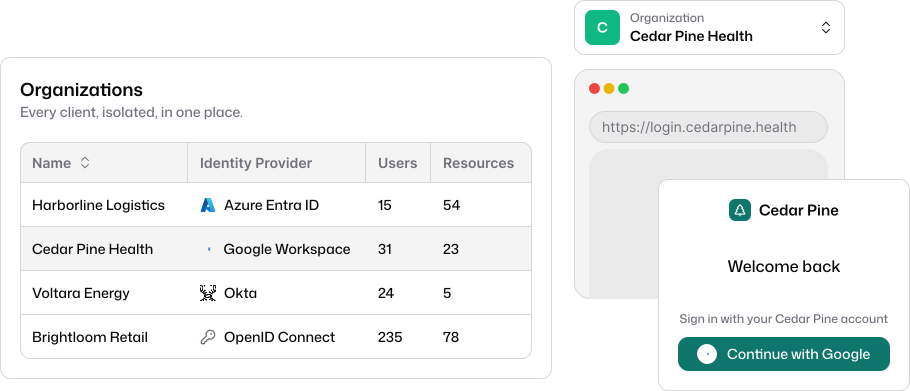
Spin up a fully isolated organization for each client, with its own users, sites, and policies. Onboard a new client in minutes without touching anyone else's environment.
Isolated by default
Every site, resource, and client belongs to one organization, so nothing leaks between customers.
Each client's own identity provider
Connect an organization-scoped identity provider so client staff sign in with the accounts they already have.
Every client in one table
When you self-host, see every organization with its owner and its user, site, and resource counts from the server admin panel.
Make it feel like your own tool
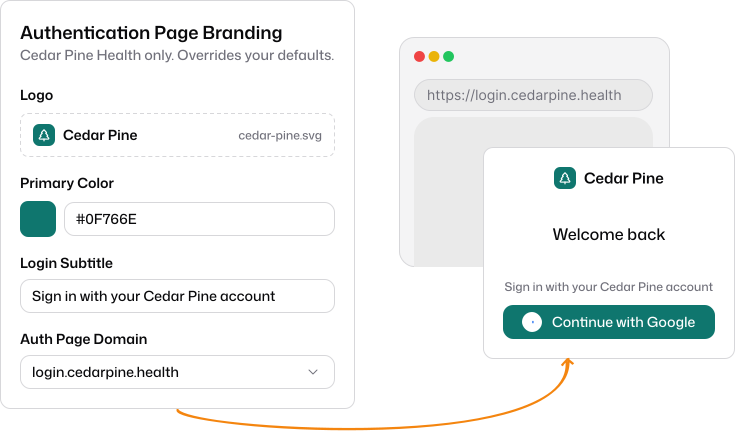
Apply your own branding and logo so the access experience looks like part of your stack, not a third-party product your clients have to be introduced to.
Your logo and colors
Set your app name, logos, and colors across the dashboard and sign-in pages.
Per-client login pages
Brand each organization's authentication pages separately to match the client.
Custom domains
Serve a client's login page from a domain you choose instead of a Pangolin URL.
Build repeatable and declarative configs
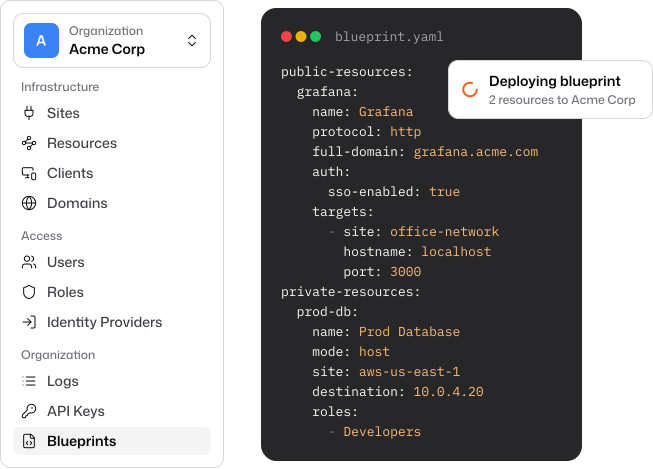
Use the integration API or declarative YAML files to create customer environments from a blueprint instead of manually. Automate it into your CI workflow and keep it in git.
Blueprints as the source of truth
Describe sites, resources, and access rules in YAML or container labels, and Pangolin keeps them in sync.
Apply from CI or the CLI
Run the same blueprint for every new client from a pipeline or a terminal.
API keys across organizations
Scope API keys to one client, or use root keys on self-hosted Pangolin to automate every organization.
Why MSPs run their clients on Pangolin
Deliver secure, modern remote access to every client you manage without adding headcount or operational overhead to your team.
Reduce complexity
Stop thinking in terms of networks and IPs and instead think about applications, users, and groups. From there the network just gets the job done.
Stand behind the security
Built on WireGuard and SOC2 II and ISO27001 certified. Identity and encryption is at the networking layer, so you can put your name behind the access you're delivering and meet compliance needs.
Own the whole stack
Pangolin is self-hostable meaning you can run the whole stack from server to client on your infrastructure and audit whats running
Completely open-source
All components of Pangolin are completely open-source. All code can be found and audited on our GitHub from the server to the end user clients.
- -90%
- Reduction in deployment time
- 100+
- Hours of support time saved
- <10min
- Time to provision a new client organization
What MSPs are saying
“I showed them Pangolin and they were mind blown.”
“We are very happy with the platform... Pangolin gives secure remote access to servers without traditional VPNs.”
Explore other use cases
Remote Access
Identity-based access to private apps, servers, and networks.
Business VPN
Replace your legacy VPN with zero trust built on WireGuard®.
Reverse Proxy
Publish internal apps behind identity, without opening ports.
Securing AI
Identity-aware access to cloud and self-hosted models.
Zero Trust & Identity
Identity providers, roles, privileged access, and audit.
Privileged Access
Just-in-time SSH, browser RDP and VNC, and session logs.