One identity and policy model for every resource
Bring your identity provider, assign access with roles, govern privileged sessions, and keep an audit trail of every decision, across apps, servers, networks, and AI.


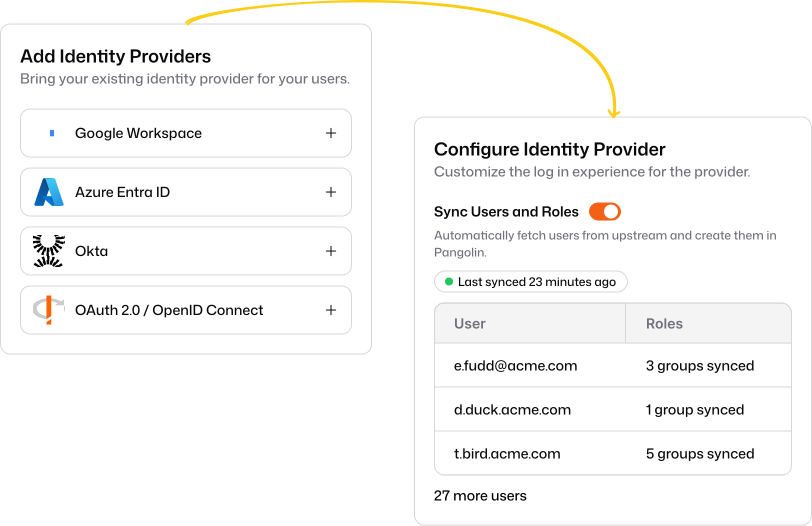
Bring your identity provider
Users sign in with the identity provider you already run, and Pangolin keeps their access in step with it.
SSO and MFA
Connect Google Workspace, Microsoft Entra ID, Okta, or any OIDC provider.
Automatic provisioning
Create users and map them to roles from your IdP the first time they sign in.
Session revalidation
Recheck sessions against your IdP so access ends when someone is offboarded.
Users, roles, and least privilege
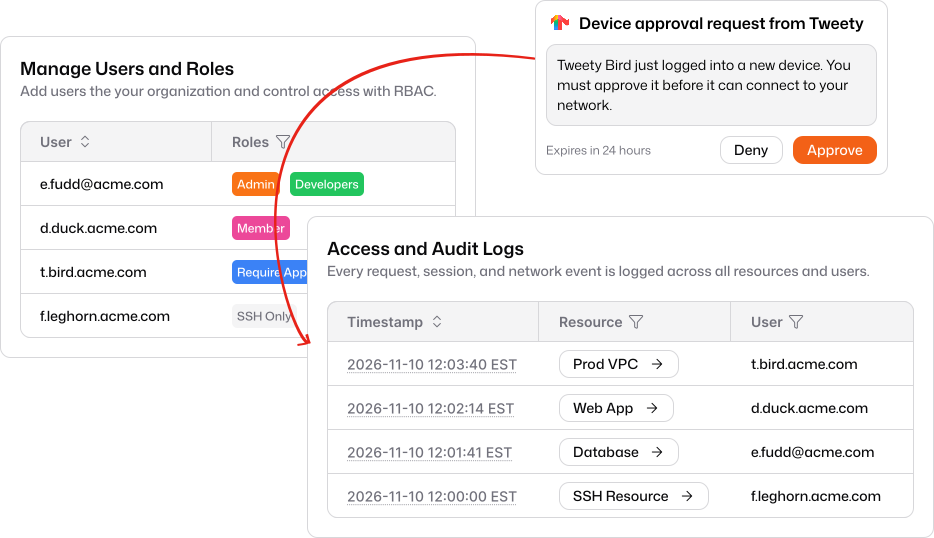
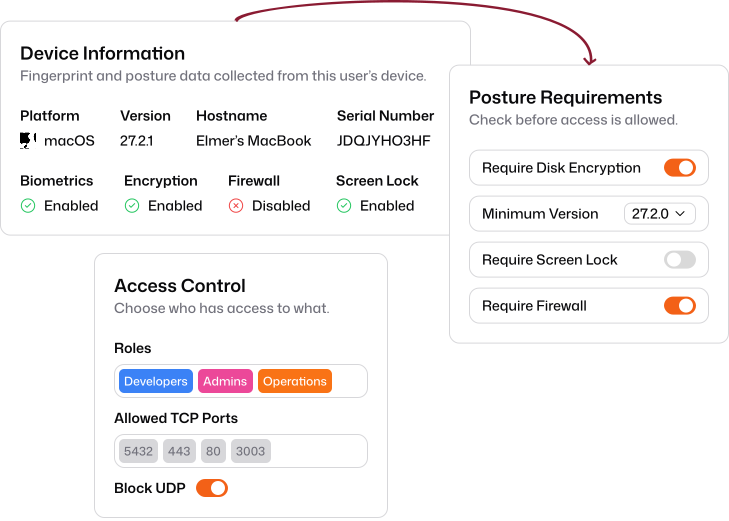
Access is granted per resource and nothing is reachable by default. A user’s access is exactly the union of what their roles can reach.
Multiple roles per user
Compose access from roles instead of maintaining one-off exceptions.
Device posture and approvals
Check devices before they connect, and approve new devices before they get any access.
Managed as code
Define roles and resources in declarative blueprints or the integration API.
Privileged access management
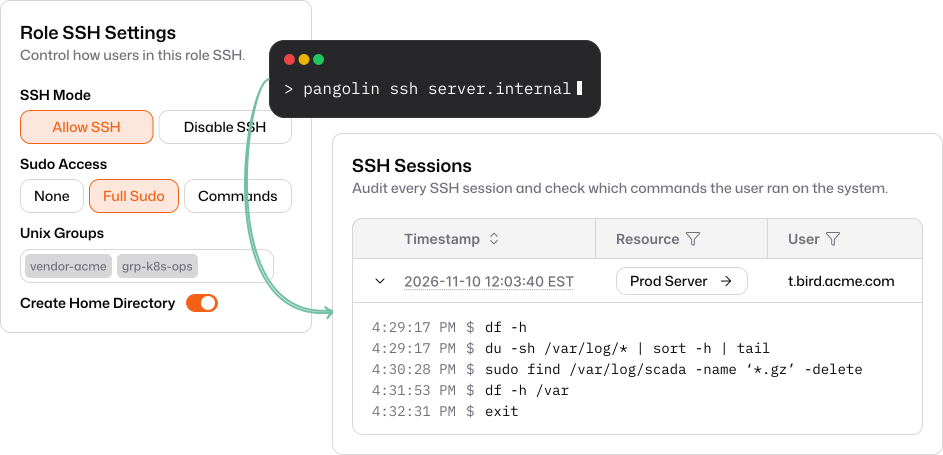
Control who can reach production servers and what they can do there, without sharing keys or running a jump box.
Role-based SSH management
Decide which roles can SSH to which hosts, with no long-lived keys to distribute.
SSH, RDP, and VNC in the browser
Open privileged sessions from the browser behind the same sign-in and rules.
SSH session logs
Keep a record of every privileged session for review and incident response.
Audit everything
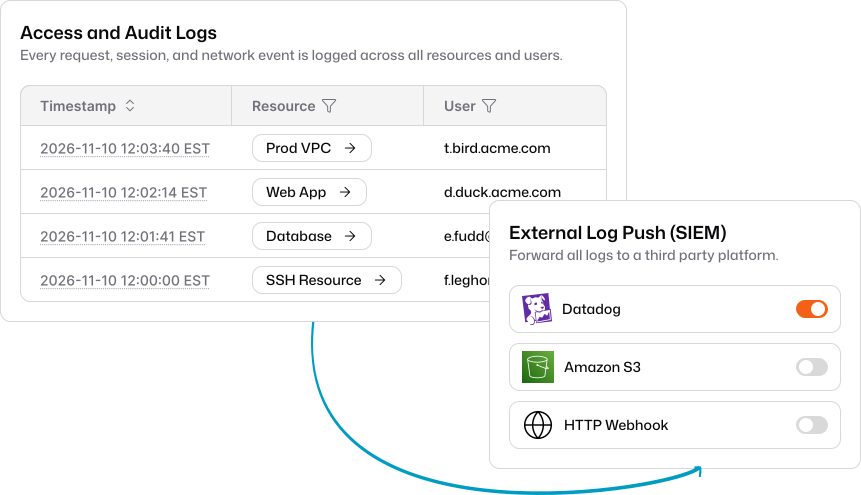
Know who accessed what, when, and from where, and who changed the policies that allowed it.
Authentication and access logs
See every sign-in and access decision across public and private resources.
Admin action logs
Track every change to users, roles, resources, and settings.
Stream to your SIEM
Export logs or stream them to your SIEM, with configurable retention.
Explore other use cases
Remote Access
Identity-based access to private apps, servers, and networks.
Business VPN
Replace your legacy VPN with zero trust built on WireGuard®.
Reverse Proxy
Publish internal apps behind identity, without opening ports.
Securing AI
Identity-aware access to cloud and self-hosted models.
Privileged Access
Just-in-time SSH, browser RDP and VNC, and session logs.