The business VPN, rebuilt for zero trust
Replace your VPN with one fast, secure, and easy to use WireGuard®-based solution. Connect people to the resources they need, not to the whole network.


Deploy in minutes
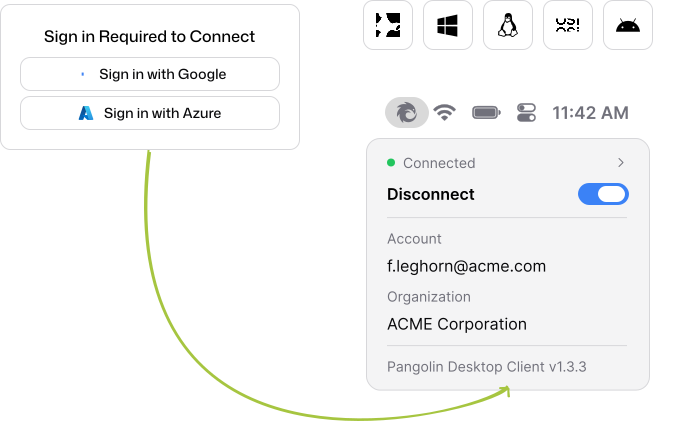
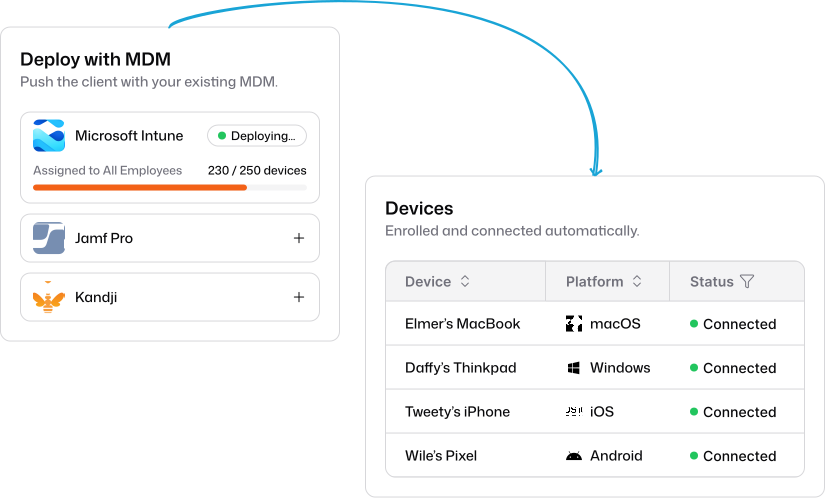
Run a lightweight connector in each network and install the client on each device. There are no firewall rules to write and no concentrators to scale.
Connectors that run anywhere
Deploy a site as a binary or container on almost any platform, from a cloud VM to an edge device.
Clients for every platform
Pangolin clients are available for macOS, Windows, Linux, iOS, and Android.
No inbound ports
Sites connect outbound, so you never open a port or expose a public IP.
Zero trust instead of a flat network
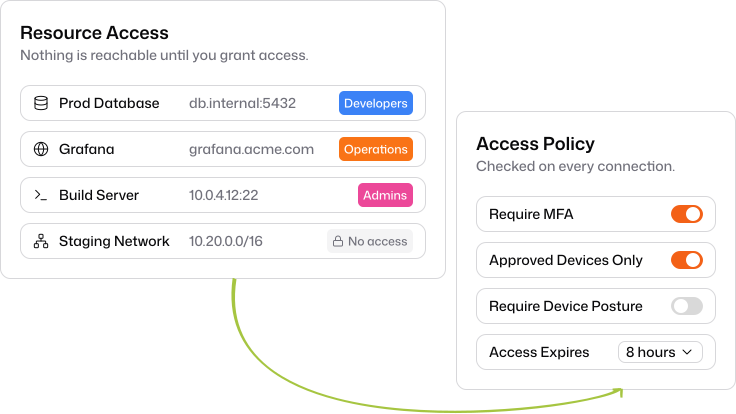
Traditional VPNs put users on the network and trust them. Pangolin grants access to specific resources and denies everything else.
Deny by default
Nothing is reachable until you define a resource and grant access to it.
Access per resource
Users and roles get the hosts, ports, and ranges they need, not the subnet around them.
Sessions that follow identity
Revalidate sessions with your IdP and set session duration and 2FA policies.
Bring your identity provider
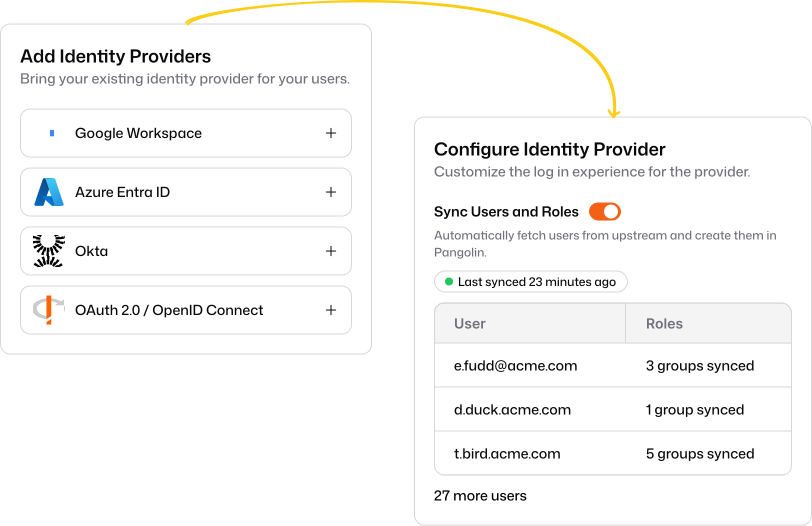
Employees sign in to the VPN with the accounts they already use, and access follows them as they join, move teams, or leave.
SSO and MFA
Connect Google Workspace, Microsoft Entra ID, Okta, or any OIDC provider.
Users and roles synced
Provision users and map their groups to roles automatically, with no separate VPN accounts to manage.
Offboarding that sticks
Disable someone in your IdP and their VPN access ends with it.
Fast, direct connections
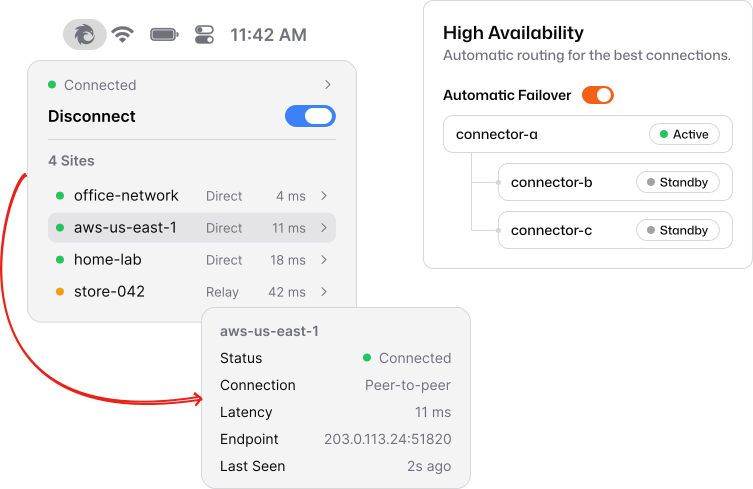
Peer-to-peer tunnels keep traffic off a central concentrator, so users get lower latency and better throughput.
Peer-to-peer by default
Clients connect directly to sites using NAT traversal, even behind restrictive firewalls.
Encrypted relay fallback
When a direct path isn’t possible, traffic relays through a node and stays encrypted end to end.
High availability
Route resources through multiple sites and fail over automatically when one goes offline.
What changes when you replace your VPN
Teams move to Pangolin to cut risk, cut busywork, and stop paying for infrastructure that slows everyone down.
| Capability | Pangolin | Traditional VPN |
|---|---|---|
| A stolen login can’t roam your whole network | Yes | No |
| Nothing on your network is exposed to the internet | Yes | No |
| Contractors get access without installing anything | Yes | No |
| Fast connections with no central bottleneck | Yes | No |
| Offboard someone once, everywhere | Yes | Varies |
| AI agents follow the same rules as people | Yes | No |
| Prove who accessed what, for every audit | Yes | Varies |
| No lock-in: run it yourself or in our cloud | Yes | Varies |
Explore other use cases
Remote Access
Identity-based access to private apps, servers, and networks.
Reverse Proxy
Publish internal apps behind identity, without opening ports.
Securing AI
Identity-aware access to cloud and self-hosted models.
Zero Trust & Identity
Identity providers, roles, privileged access, and audit.
Privileged Access
Just-in-time SSH, browser RDP and VNC, and session logs.